Moxa — VPN peer design, fiber interfaces and rugged-site review for EDR-G9010-VPN-2MGSFP-T
| Device role | industrial secure router |
|---|---|
| Product model | EDR-G9010-VPN-2MGSFP-T |
| Key configuration | Document VPN peers and protected subnets |
| Interface check | Verify each management and data interface |
| Installation | Match fiber transceivers to the route |
| Acceptance | Test failover and recovery under site policy |
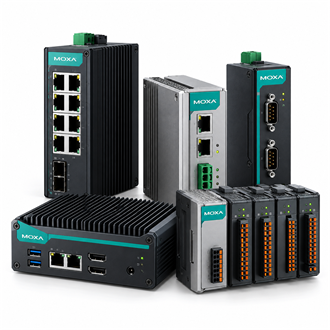
The EDR-G9010-VPN-2MGSFP-T is considered here as a industrial secure router. Industrial secure-router model with vpn in the ordering code; verify fiber/copper interfaces, vpn peer requirements, security policy and full temperature/power details for the specific suffix.. Before selecting the EDR-G9010-VPN-2MGSFP-T, map the complete path from field signals and network boundaries to the host system, supply source and operating location.
Start with the topology
When the EDR-G9010-VPN-2MGSFP-T is part of a migration, record the old interface and behavior before disconnection. Note timing, addressing, scaling and fail-state behavior, then compare these with the new EDR-G9010-VPN-2MGSFP-T configuration under a controlled test. Preserve a rollback path until the application owner accepts the observed result and the maintenance team has the final record.
Check the physical layer
The information needed to quote a EDR-G9010-VPN-2MGSFP-T accurately includes the full model code, quantity, installation country, host platform, network or fieldbus details, environmental conditions and any required accessories. Include a wiring sketch or port schedule where useful. This lets a reviewer confirm whether the selected EDR-G9010-VPN-2MGSFP-T and its variant align with the actual installation.
Configuration checkpoints
For a EDR-G9010-VPN-2MGSFP-T enquiry, begin with the device that must connect, the protocol on each side and the owner of the communication session. Record the required direction of data flow and identify whether the EDR-G9010-VPN-2MGSFP-T is expected to initiate requests, respond to a controller or simply pass traffic. These details determine a workable configuration more reliably than a model-family name alone.
Acceptance tests
The physical design around EDR-G9010-VPN-2MGSFP-T should be checked before commissioning. Confirm connector type, cable medium, termination, grounding, power availability and any environmental suffix. A nominal protocol match does not guarantee the cable or electrical interface is compatible; document each endpoint and its pin or port assignment before energizing the EDR-G9010-VPN-2MGSFP-T.
Order review
During integration, configure the EDR-G9010-VPN-2MGSFP-T against an approved network plan rather than assigning addresses informally at the cabinet. Capture VLAN or subnet boundaries where applicable, device names, serial settings, firmware baseline and the expected diagnostics. A commissioning record makes later service work on the EDR-G9010-VPN-2MGSFP-T much faster and helps separate wiring faults from application mapping errors.
Start with the topology
A staged acceptance test for EDR-G9010-VPN-2MGSFP-T should prove the local link first, then the protocol exchange and finally the full application value. Compare a known input or register with the value at the consuming system, check alarm behavior, and record recovery after a controlled link interruption where site procedures permit. Save the result with the exact EDR-G9010-VPN-2MGSFP-T identifier.
Check the physical layer
For replacement planning, retain the EDR-G9010-VPN-2MGSFP-T part code, suffix, connector details, firmware and accessory list alongside the as-built drawing. If the site has an established configuration, compare it with the proposed EDR-G9010-VPN-2MGSFP-T replacement before changing the device; small suffix differences can affect temperature, optical interface, power input or included cable options.
Configuration checkpoints
The EDR-G9010-VPN-2MGSFP-T selection should also account for maintenance access. Identify who owns firmware updates, where configuration backups are stored and how alarms reach the operations team. If several EDR-G9010-VPN-2MGSFP-T devices are deployed, keep one inventory row per physical unit with its location, address, attached equipment and validated configuration instead of relying on an unstructured label list.
Acceptance tests
Before issuing a purchase order for EDR-G9010-VPN-2MGSFP-T, ask the site team to verify the complete nameplate, target application, environmental range and required accessories. Confirm that the quantity covers the installed topology and any approved spare policy. This final review reduces avoidable substitutions and keeps the delivered EDR-G9010-VPN-2MGSFP-T aligned with the approved bill of materials.
Order review
Keep the EDR-G9010-VPN-2MGSFP-T design within documented operating limits and the project's cybersecurity and safety procedures. Apply only approved network services, protect management access, use the required grounding and isolation practices, and validate the finished installation against current manufacturer documentation. The EDR-G9010-VPN-2MGSFP-T should be treated as one element in a system-level design, not as a substitute for the system review.
Order review
- EDR-G9010-VPN-2MGSFP
- EDR-G9010-VPN-2MGSFP-HV-T
